
Table of Contents
DevOps Maturity Assessment: A Guide for Enterprises
Modern enterprises depend on software systems to deliver customer experiences, support business operations, process transactions and maintain competitive advantages. As applications become more complex, organisations must find ways to release software reliably, respond to incidents quickly and coordinate development and operations teams effectively.
However, adopting DevOps tools does not automatically create an efficient software delivery environment. An organisation may use cloud platforms, automated testing and continuous integration pipelines while still experiencing delayed releases, recurring incidents, manual approvals and communication gaps.
A DevOps Maturity Assessment helps organisations understand how effectively their development, operations, testing, security and delivery practices work together. It establishes a structured view of current capabilities, identifies weaknesses and supports a practical roadmap for improvement.
For enterprise technology leaders, the purpose is not simply to determine whether their organisation has reached a particular maturity level. It is to understand which improvements will make the greatest difference to delivery speed, software quality, operational stability and business outcomes.
This guide explains how a DevOps maturity assessment works, which capabilities should be evaluated, how organisations can measure progress and how to turn assessment findings into an achievable transformation plan.
What Is a DevOps Maturity Assessment?
A DevOps maturity assessment is a structured evaluation of an organisation’s software delivery capabilities, engineering practices, automation, collaboration, governance and operational performance.
It examines how development and operations teams plan, build, test, release, monitor and maintain software. Depending on the organisation’s needs, it may also evaluate security integration, cloud infrastructure, platform engineering, service reliability and the management of legacy applications.
The assessment compares current practices against defined criteria, relevant industry practices and the organisation’s own business objectives.
For example, an enterprise might discover that its developers use automated build pipelines but rely on manual regression testing before production releases. Another organisation might have strong deployment automation but lack consistent monitoring and incident analysis.
Both organisations use DevOps tools, but their delivery capabilities have different constraints.
A structured assessment helps identify these differences and establish priorities based on evidence rather than assumptions.
Why is DevOps maturity important?
DevOps maturity matters because software delivery depends on several connected capabilities. Automation alone cannot compensate for unclear ownership, unreliable test environments, inadequate monitoring or slow decision-making.
A mature operating model generally supports:
- More consistent software delivery processes.
- Better visibility into release readiness.
- Earlier identification of software defects.
- Improved collaboration across engineering teams.
- More reliable incident detection and recovery.
- Repeatable infrastructure and deployment practices.
- Appropriate security and compliance controls.
- Continuous learning from delivery and operational data.
Maturity should not be confused with the number of tools an organisation owns. The important question is whether its people, processes and technology consistently support the outcomes the business requires.
Why Enterprises Need a DevOps Maturity Assessment
Enterprise technology environments often contain multiple applications, shared infrastructure, third-party dependencies, regulatory requirements and teams working across different locations.
These conditions can make delivery problems difficult to diagnose.
1. Identifying software delivery bottlenecks
A software release may involve development, code review, automated testing, security checks, business approvals and production deployment. If one stage depends on manual work or an overloaded team, the entire process can slow down.
A maturity assessment maps these stages and examines waiting times, repeated work, failed handoffs and avoidable dependencies.
2. Evaluating automation effectiveness
Installing a CI/CD platform is only one step towards automation. Teams may still maintain fragile scripts, repeat manual tests or perform deployments differently across applications.
The assessment examines whether automation is reliable, maintainable, repeatable and suitable for the organisation’s delivery risks.
3. Improving reliability and operational readiness
Fast releases provide limited value if production systems become unstable or incidents take too long to resolve.
Evaluating monitoring, alert quality, incident response, service ownership and recovery practices helps enterprises understand whether their operational capabilities support their release objectives.
4. Managing security and compliance
Enterprises in banking, insurance, telecommunications and other regulated environments must balance delivery efficiency with appropriate controls.
An assessment can examine how security testing, access management, audit trails, approval policies and evidence collection are integrated into the software delivery lifecycle.
The goal is to identify opportunities for consistent, risk-based controls rather than removing necessary governance.
5. Creating a measurable transformation roadmap
Without a baseline, teams may select improvement projects based on the latest technology trend or the preferences of individual departments.
A maturity assessment establishes a starting point, helping leadership prioritise initiatives according to business impact, implementation effort, risk and dependencies.
Key Dimensions of a DevOps Maturity Assessment
A useful assessment examines the complete delivery system rather than focusing exclusively on tools.
1. Culture and collaboration
DevOps depends on cooperation between development, operations, quality engineering, security and business stakeholders.
The assessment should examine whether teams share responsibility for delivery outcomes, communicate effectively and learn from failures.
Useful questions include:
- Are responsibilities clearly defined across the software lifecycle?
- Do teams share delivery and reliability objectives?
- Are incidents investigated to identify systemic causes?
- Can engineers raise delivery risks without blame?
- Are operational lessons incorporated into development practices?
Siloed responsibilities, inconsistent communication and competing departmental objectives can undermine otherwise capable engineering teams.
2. Continuous integration and delivery
CI/CD practices help organisations integrate code changes frequently, test them consistently and automate appropriate release activities.
An assessment should evaluate build reliability, pipeline duration, test execution, deployment repeatability, release approvals and rollback procedures.
It should also examine whether pipelines are standardised appropriately or require extensive application-specific maintenance.
The objective is not to automate every decision. It is to remove unnecessary manual effort while retaining controls that address genuine business, security or regulatory risks.
3. Test automation and quality engineering
Testing is a major consideration in enterprise DevOps maturity because unreliable or slow testing can delay releases and increase production risk.
Assessment areas include automated unit, integration, API, regression and end-to-end testing, where appropriate.
Teams should examine test coverage of critical business behaviour, test stability, execution time, defect escape rates and maintenance effort.
Test data availability and environment consistency also matter. Automated tests cannot provide dependable feedback when they depend on unreliable data or environments that differ significantly from production.
4. Infrastructure and configuration management
Infrastructure automation supports consistent environments and repeatable deployments.
A maturity assessment may examine infrastructure as code, configuration management, environment provisioning, secrets handling, access controls and drift detection.
Enterprises should determine whether infrastructure changes are version-controlled, reviewed and reproducible.
These practices are particularly useful where teams maintain multiple environments, support complex integrations or manage hybrid and cloud-based systems.
5. Monitoring, observability and SRE
Operational visibility is essential for understanding application behaviour and identifying emerging problems.
The assessment should evaluate metrics, logs, traces, alerting, service-level indicators and service-level objectives where appropriate.
It should also consider incident ownership, escalation procedures, recovery plans and post-incident learning.
Site Reliability Engineering (SRE) practices can help teams balance delivery changes with reliability requirements. However, the appropriate implementation depends on service criticality, organisational structure and available engineering resources.
6. Security and governance
Security should be integrated into the delivery lifecycle instead of being treated exclusively as a final release checkpoint.
Relevant assessment areas include dependency scanning, code security testing, secrets management, access permissions, vulnerability remediation and auditability.
For regulated organisations, governance requirements should be mapped to applicable jurisdictions, contractual obligations and internal policies.
A strong assessment distinguishes necessary risk controls from avoidable process delays and identifies opportunities to automate evidence collection and repeatable checks.
7. Measurement and continuous improvement
Engineering teams need reliable information to determine whether changes improve delivery performance.
The assessment should review the quality, consistency and use of metrics such as deployment frequency, change lead time, change failure rate and failed deployment recovery time.
These measures are useful only when interpreted in context. For example, deployment frequency varies by application type, release strategy and business risk.
The objective is to improve the delivery system rather than encourage teams to optimise individual numbers at the expense of quality or reliability.
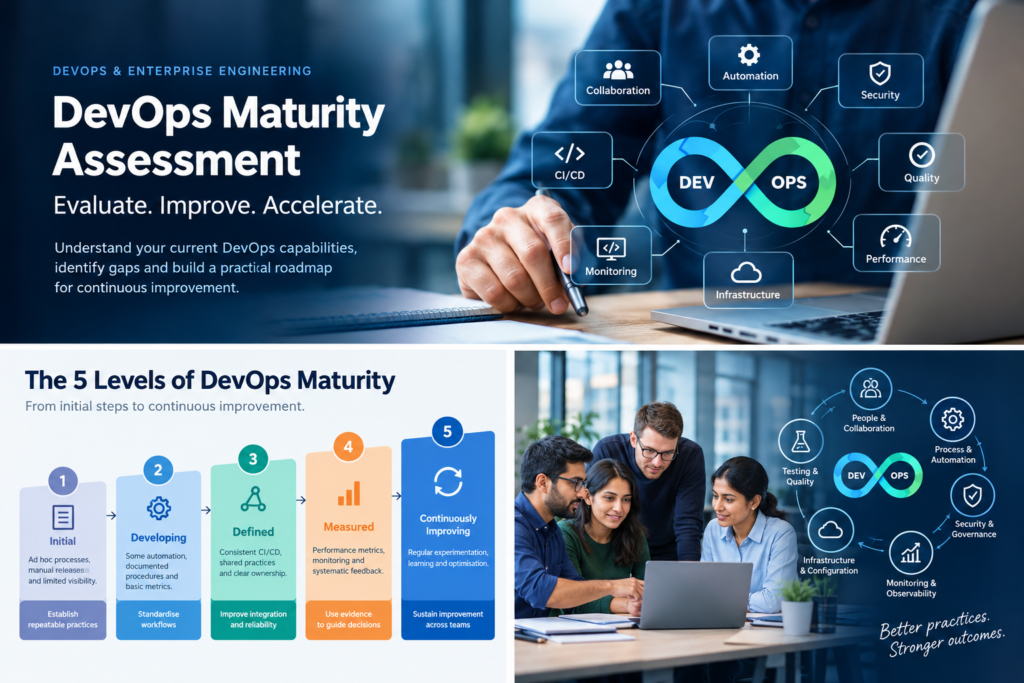
Understanding DevOps Maturity Levels
Organisations can use a staged maturity model to communicate current capabilities and define improvement priorities. The following five-level framework is an illustrative model, not a claim that every enterprise must follow the same progression.
| Level | Typical characteristics | Main improvement priority |
|---|---|---|
| 1. Initial | Ad hoc processes, manual releases and limited visibility | Establish repeatable practices |
| 2. Developing | Some automation, documented procedures and basic metrics | Standardise workflows |
| 3. Defined | Consistent CI/CD, shared practices and clear ownership | Improve integration and reliability |
| 4. Measured | Performance metrics, monitoring and systematic feedback | Use evidence to guide decisions |
| 5. Continuously improving | Regular experimentation, learning and optimisation | Sustain improvement across teams |
Level 1: Initial
At this stage, delivery often depends on individual knowledge and manual coordination. Processes may vary considerably between applications.
The first priority is to document critical workflows, establish ownership, introduce version control consistently and identify the highest-risk manual activities.
Level 2: Developing
Teams begin automating builds, testing or deployments, but practices may differ across departments.
Improvement should focus on reusable pipeline patterns, reliable test environments, basic monitoring and clear release procedures.
Level 3: Defined
Standard delivery practices are established across relevant teams. Automation, testing, security and operational processes are integrated more consistently.
The organisation can now focus on reducing unnecessary variation and improving the reliability of shared engineering capabilities.
Level 4: Measured
Teams use delivery and operational metrics to identify bottlenecks and evaluate improvement initiatives.
The priority is to ensure that measurements support sound decisions, with clear definitions and appropriate context.
Level 5: Continuously improving
Teams regularly evaluate outcomes, learn from incidents, test improvements and refine engineering practices.
Reaching this stage does not mean that all processes should be fully automated or that no further improvement is needed. Continuous improvement remains an ongoing activity.
How to Conduct a DevOps Maturity Assessment
A structured assessment should produce evidence-based findings and an actionable roadmap.
Step 1: Define business objectives and scope
Begin by identifying why the assessment is being conducted.
Objectives might include reducing release delays, improving production reliability, increasing test automation, standardising cloud deployments or strengthening security controls.
Define which applications, teams, environments and delivery processes will be included. For a large organisation, a representative pilot may provide a practical starting point.
Step 2: Collect evidence
Use multiple sources to understand actual practices.
These may include interviews, engineering workshops, pipeline configurations, deployment records, incident reports, test results, architecture documentation and delivery metrics.
Avoid relying entirely on self-reported maturity scores. Teams may describe a process as automated even when important stages remain manual or unreliable.
Step 3: Evaluate each capability
Score relevant dimensions using consistent, documented criteria.
For example, a team might receive a stronger score for CI/CD when builds are repeatable, automated tests provide dependable feedback, deployments are controlled and failures can be investigated efficiently.
Document evidence supporting each score, including strengths, limitations and unresolved questions.
Step 4: Identify gaps and root causes
Distinguish symptoms from underlying problems.
A slow release process might result from lengthy regression tests, unavailable test environments, unclear approval responsibilities or fragile deployment scripts.
Addressing the root cause is more useful than automatically purchasing another tool.
Step 5: Prioritise improvement opportunities
Rank initiatives using factors such as business impact, implementation effort, delivery risk, dependencies and available skills.
Quick improvements may include standardising pipeline templates or improving alert quality. Larger initiatives might involve redesigning test environments, modernising legacy applications or introducing shared platform capabilities.
Step 6: Build a phased roadmap
Translate findings into practical initiatives with accountable owners, milestones and measurable outcomes.
A roadmap should include technical work, team enablement, governance considerations and the resources required to sustain the changes.
Step 7: Measure progress and reassess
Repeat relevant measurements after improvements have been implemented.
Compare results against the original baseline and investigate unexpected outcomes. Reassessment should reflect meaningful changes in capabilities rather than simply aiming to increase a maturity score.
Metrics to Include in a DevOps Maturity Assessment
Metrics help establish whether engineering practices support business objectives.
| Metric | What it helps evaluate | Important consideration |
|---|---|---|
| Deployment frequency | How often changes reach production | Compare suitable applications and release models |
| Change lead time | Time from a code change to production | Define start and end points consistently |
| Change failure rate | Proportion of changes resulting in failures | Use a consistent definition of failure |
| Failed deployment recovery time | Time needed to recover from failed deployments | Document recovery start and end points |
| Build success rate | Reliability of build processes | Separate infrastructure failures from code failures |
| Automated test reliability | Consistency of automated test results | Investigate flaky tests and environment issues |
| Defect escape rate | Defects identified after release | Interpret alongside severity and testing scope |
| Service availability | Ability of a service to meet availability expectations | Use agreed measurement windows and service objectives |
The first four metrics are commonly associated with DORA software delivery performance research. Organisations should consult current DORA guidance for precise definitions and interpret results within their context.
Metrics should not become isolated targets. Increasing deployment frequency, for example, is not necessarily beneficial if the change failure rate or customer impact also increases.
Common DevOps Maturity Assessment Challenges
Treating maturity as a competition
Comparing teams using a single score can conceal differences in application complexity, service criticality and regulatory obligations.
Use assessments to identify opportunities for improvement, not to shame teams or create arbitrary rankings.
Focusing only on technology
Tools are important, but culture, ownership, skills, communication and governance also influence outcomes.
A technically advanced pipeline may still be ineffective if teams cannot maintain it or if organisational processes repeatedly delay releases.
Using inconsistent scoring criteria
If different assessors interpret maturity levels differently, results become difficult to compare.
Use documented definitions, evidence requirements and calibration sessions to improve consistency.
Automating inefficient processes
Automation can reproduce existing inefficiencies at greater speed.
Simplify workflows and clarify decision-making before automating unnecessary steps.
Failing to follow through
An assessment that ends with a presentation but no accountable owners rarely produces sustained change.
Each significant finding should connect to a decision, an action, a responsible owner and a way to measure progress.
How Sandhata Technologies Relates to DevOps Maturity Assessment
Sandhata Technologies presents enterprise engineering capabilities that include DevOps, Site Reliability Engineering, Quality Engineering, automation and related technology services.
These areas are relevant when organisations need to evaluate how their software delivery processes operate as a connected system.
For example, a maturity improvement programme may involve reviewing CI/CD practices, identifying test automation gaps, improving operational observability or examining the reliability of deployment workflows.
The appropriate scope depends on the organisation’s applications, delivery constraints, operating model and business priorities. Assessment findings should determine which services or technical interventions are relevant.
Enterprises considering external support can review Sandhata Technologies’ official website to understand its published capabilities and identify relevant service information.
When evaluating any consulting provider, decision-makers should clarify the proposed assessment framework, evidence-gathering process, deliverables, team responsibilities, confidentiality arrangements and method for measuring improvement.
The most useful outcome is a practical, prioritised plan that the organisation can implement and reassess over time.
Conclusion
A DevOps Maturity Assessment gives enterprise organisations a structured way to evaluate software delivery practices, identify operational constraints and prioritise engineering improvements.
An effective assessment examines culture, CI/CD, quality engineering, infrastructure, security, observability and measurement. It uses evidence to distinguish genuine capability gaps from assumptions and turns findings into a phased roadmap.
For UK and global enterprises, the right approach should reflect business objectives, application criticality, regulatory obligations and existing technical capabilities. A maturity score is useful as a baseline, but the lasting value comes from measurable improvements to delivery reliability, engineering efficiency and operational performance.
Organisations should therefore treat assessment as the beginning of a continuous improvement process, supported by clear ownership, meaningful metrics and regular evaluation of results.
Frequently Asked Questions
1. What is a DevOps maturity assessment?
A DevOps maturity assessment evaluates an organisation’s software delivery practices, automation, collaboration, testing, security and operational reliability. It identifies current strengths and weaknesses and helps create a prioritised improvement roadmap.
2. Why should an enterprise conduct a DevOps maturity assessment?
Enterprises use assessments to identify delivery bottlenecks, understand automation gaps, improve release consistency, strengthen operational practices and align engineering improvements with business objectives.
3. How often should DevOps maturity be assessed?
The frequency depends on organisational needs. An enterprise might conduct an initial assessment, review progress after significant improvement initiatives and perform periodic reassessments. Changes to architecture, teams or business requirements may also justify a review.
4. What are the main dimensions of a DevOps maturity assessment?
Common dimensions include culture and collaboration, CI/CD, test automation, infrastructure management, security, monitoring, incident response and continuous improvement. The exact framework should reflect the organisation’s objectives.
5. What are the five levels of DevOps maturity?
An illustrative five-level model includes initial, developing, defined, measured and continuously improving. These levels describe increasing consistency, automation, measurement and learning, but terminology varies between assessment frameworks.
6. How long does a DevOps maturity assessment take?
The duration depends on the number of applications, teams, locations and technical environments involved. A narrowly scoped assessment may take considerably less time than an enterprise-wide review. Agree on scope, evidence requirements and deliverables before beginning.
7. Which metrics are useful for assessing DevOps maturity?
Useful metrics include deployment frequency, change lead time, change failure rate, failed deployment recovery time, build reliability, test stability and service availability. Metrics should have consistent definitions and be interpreted in context.
8. Is DevOps maturity assessment suitable for small engineering teams?
Yes. Smaller teams can use a simplified assessment to review deployment practices, automated testing, monitoring, security and ownership. The framework should remain proportionate to the team’s size, architecture and operational risks.
9. How does CI/CD affect DevOps maturity?
CI/CD supports repeatable integration, testing and deployment. Its contribution to maturity depends on pipeline reliability, test quality, deployment controls, feedback speed and maintainability rather than the mere presence of automation tools.
10. What is the difference between DevOps maturity and DevOps adoption?
DevOps adoption refers to introducing DevOps practices or tools. DevOps maturity concerns how consistently and effectively those practices work across the organisation and how well they support measurable business and engineering outcomes.
11. Can a DevOps maturity assessment help reduce deployment failures?
It can identify weaknesses associated with deployment failures, such as inadequate testing, inconsistent environments or poor rollback procedures. Improvements may reduce risk, but actual outcomes depend on implementation and ongoing measurement.
12. How does Site Reliability Engineering relate to DevOps maturity?
SRE introduces practices for managing reliability, service objectives, monitoring, incident response and operational risk. Evaluating these capabilities can help organisations understand whether their delivery processes adequately support production services.
13. Should security be included in a DevOps maturity assessment?
Yes. Security evaluation may cover access management, dependency scanning, code analysis, secrets handling, vulnerability remediation and audit trails. The assessment should reflect the organisation’s threat model and applicable regulatory requirements.
14. Can DevOps maturity assessment help with legacy systems?
Yes. It can identify constraints involving manual releases, limited test automation, integration dependencies, environment management and operational visibility. Modernisation priorities should reflect system criticality, technical feasibility and business requirements.
15. What is the role of test automation in DevOps maturity?
Test automation helps teams obtain repeatable feedback about software changes. Assessment should consider test coverage, stability, execution time, maintenance effort, test data and the ability to detect important defects before production.
16. How should enterprises choose a DevOps maturity assessment framework?
Choose a framework with clear criteria, evidence-based scoring, relevant engineering dimensions and a practical improvement methodology. Ensure that the framework accommodates application differences, regulatory obligations and the organisation’s business objectives.
17. What should a DevOps maturity assessment report contain?
A useful report includes scope, methodology, capability scores, supporting evidence, strengths, identified gaps, risks, prioritised recommendations, accountable owners and proposed success measures. It should also explain assumptions and limitations.
18. Can DevOps maturity be improved without replacing existing tools?
Yes. Improvements may come from better pipeline design, stronger test practices, clearer ownership, improved monitoring, standardised workflows and more effective use of existing platforms. Tool replacement should be based on demonstrated requirements rather than assumed necessity.
19. How can an enterprise measure improvement after an assessment?
Establish baseline metrics, implement prioritised changes and measure the same indicators consistently over time. Review both delivery performance and quality outcomes, and account for changes in application scope, release strategy and operational conditions.
20. How can organisations evaluate external DevOps assessment providers?
Review the provider’s assessment methodology, relevant technical expertise, evidence-gathering approach, reporting format, confidentiality practices and roadmap process. Ask how recommendations will be prioritised and how progress will be measured after the assessment.